How Secure File Transfer Actually Works: End-to-End Protection, MFA, and Audit Trails Explained
—

In today’s digital economy, data is both your most valuable and most vulnerable asset. Yet many organizations still share sensitive documents the same way they did twenty years ago: as standard email attachments.
Hitting “Send” feels instant and free, but the hidden cost of unsecured file sharing can be devastating. Regulatory fines, incident investigations, and reputation damage all trace back, surprisingly often, to a simple attachment. This guide explains what secure file transfer really means and how to strengthen security and compliance without slowing the business down.
Why Secure Business File Sharing Beats Email Attachments
Email was built for open communication, not controlled distribution of sensitive content. The moment you attach a file, you create an uncontrolled copy.
The “Vaporization” of Control: Once an attachment leaves your outbox, you lose visibility. You cannot see who has downloaded it, how many times it’s been opened, or where it’s been saved.
The Domino Effect: Attachments can be forwarded to unauthorized recipients, stored on unmanaged personal devices, or exposed when a single inbox is compromised.
The Compliance Gap: Modern security frameworks (HIPAA, GDPR, SOC 2, ISO 27001, etc.) assume you can prove what happened to a sensitive file. If you cannot show who accessed it, when, and under what controls, you are effectively out of compliance.
Secure business file transfer replaces uncontrolled copies with controlled access. Instead of sending the file itself, you send a governed, auditable way to reach it.
What “Secure File Transfer” Really Means
Modern secure file transfer flips the model: you do not ship the document out into the world; you deliver controlled, identity-based access to it.
That model rests on three technical layers:
Encryption in Transit (HTTPS/TLS).
Think of this as the armoured truck: it protects the data while it travels over the network so it cannot be read if intercepted
Encryption at Rest.
This is the vault: it ensures the file remains encrypted and unreadable while stored, even if someone gains access to the storage system.
Identity Verification (MFA).
Using MultiFactor Authentication, the system verifies that the person opening the link is the intended recipient, not just anyone with access to their email.
A secure file transfer approach extends these controls across desktops, laptops, and mobile devices, so users can work from anywhere without resorting to risky workarounds like personal email or consumer sync-and-share tools.
The Four Pillars of a Compliance-Ready Solution
If you are evaluating secure transfer tools, these are the pillars that matter most for audits and investigations.
1. Strong Encryption
Use modern standards such as AES256 for both data in transit and at rest.
Ensure keys are managed securely, rotated regularly, and never exposed to end users.
2. Identity and Access Controls
Require Multi-Factor Authentication (MFA) for accessing sensitive files.
Apply Role-Based Access Controls (RBAC) so only appropriate job roles can view specific data.
Regularly review and update user permissions, especially when people change roles or leave the organization.
3. Exportable Audit Trails
Capture a full “paper trail” for every file: who sent it, who viewed it, when it was downloaded, and when access was revoked.
Make that trail exportable so you can hand regulators and auditors clear evidence instead of screenshots and guesswork.
4. Policy Enforcement and Automation
Enforce default expiry dates so links and files do not live forever by accident.
Apply geographic or data residency controls where required.
Automate cleanup and access revocation so security does not depend on users remembering to “tidy up” manually.
Phishing-resistant MFA (such as FIDO2/WebAuthn methods) is rapidly becoming a standard for blocking credential-based attacks. Technical controls work best when combined with user education, including training and simulations that reinforce how to recognize phishing and handle sensitive data correctly.
Bridging the Gap: How PF360 SecureMail Applies These Principles
The biggest hurdle in security is often friction. If a tool is slow or confusing, employees will quietly route around it. PF360 SecureMail is designed to close that gap by embedding secure file transfer into the tools people already use every day.
SecureMail lets users keep working inside their familiar email environment while replacing risky attachments with secure, encrypted links.
Effortless for Senders and Recipients
No heavy client software or complicated setup.
Works from Windows, Mac, and mobile devices.
External recipients can access files through a secure link without installing software or creating complex accounts, subject to the access controls you define.
Revocation and Real Control
If a file is sent to the wrong person, you can instantly revoke the link instead of hoping the recipient “deletes the email.” Access can be time-bound, limited by the number of downloads, and locked behind MFA as required.
Integration with Office Workflows
Beyond email, SecureMail integrates with Multi-Function Devices (MFDs) from vendors such as Ricoh, Xerox, and HP. Staff can scan physical documents at the device and send them as encrypted links directly from the office scanner—ideal for healthcare, finance, and public sector workflows that still rely on paper.
Real-Time Tracking and Auditability
Every interaction with a shared file (send, view, download, expiration, revocation) is logged. These logs help healthcare, financial services, and legal teams meet SOC 2, HIPAA, and GDPR expectations without building their own tracking systems.
In short, SecureMail applies encryption, identity, audit, and policy controls without forcing users to abandon their email-centric workflow.
Checklist: Is Your File Transfer Process Audit Ready?
If you cannot confidently answer “Yes” to all of the following, your current process is likely creating avoidable risk.
Can you revoke access to a file after it has been sent?
Can you require Multi-Factor Authentication (MFA) per file or workflow?
Can you export a complete audit trail (send, view, download, revocation, completion)?
Do files and links expire automatically based on your security policies?
Do you have clear, documented controls over who can access what (RBAC), and are those permissions reviewed regularly?
If the honest answer to any of these is “no,” then legacy attachments and generic file-sharing tools leave gaps that regulators—and attackers—will eventually find.
Frequently Asked Questions About Secure File Transfer
Q: What is secure file transfer?
A: Secure file transfer is a controlled way to share sensitive files using encrypted delivery, identity-based access (often with MFA), and an audit trail that proves who accessed the file and what actions they took.
Q: What does “end-to-end protection” mean in this context?
A: In practice, it means your file is protected while it travels over the internet (encryption in transit) and while it is stored (encryption at rest), so the content is not exposed even if the network or storage systems are compromised.
Q: Why is an audit trail so important?
A: An audit trail provides hard evidence for compliance and incident investigations by recording events such as send, view, download, authentication, expiration, and revocation, all with timestamps and user identities.
Conclusion and Next Steps
In modern business, “good enough” security for file sharing is only good enough until the first breach or audit. Moving from traditional attachments to a secure file transfer approach not only protects your data but also protects your reputation and provides defensible proof of control.
If you want a secure, trackable alternative to attachments that fits naturally into your teams' existing workflows, see how PF360 SecureMail handles real-world workflows. A short walkthrough can show you exactly how encryption, MFA, and audit trails come together to make your file transfer process truly audit-ready.

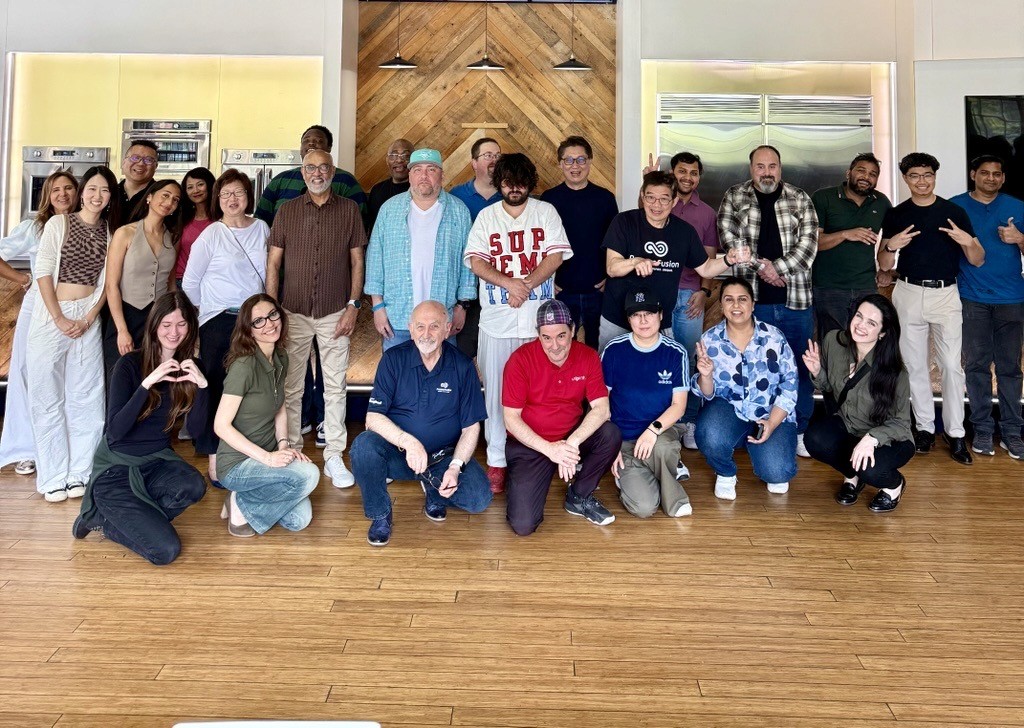
LIFE AT PROCESS FUSION
Team activities that turn colleagues into community
From social gatherings and shared celebrations to collaborative activities, we create space for people to connect beyond projects. These moments strengthen relationships, spark new ideas, and make everyday teamwork more meaningful.
01
Pride
We take pride in the work we create, the customers we support, and the positive impact we make together. Every contribution matters, and shared ownership turns good work into meaningful progress.
02
Trust
Open communication, respect, and accountability give people the confidence to contribute fully. We trust one another to share ideas honestly, follow through, and grow from every challenge.
03
Camaraderie
Shared experiences, team activities, and everyday support create genuine connection. We make room to laugh, celebrate, and help one another—building a community where people feel they belong.


